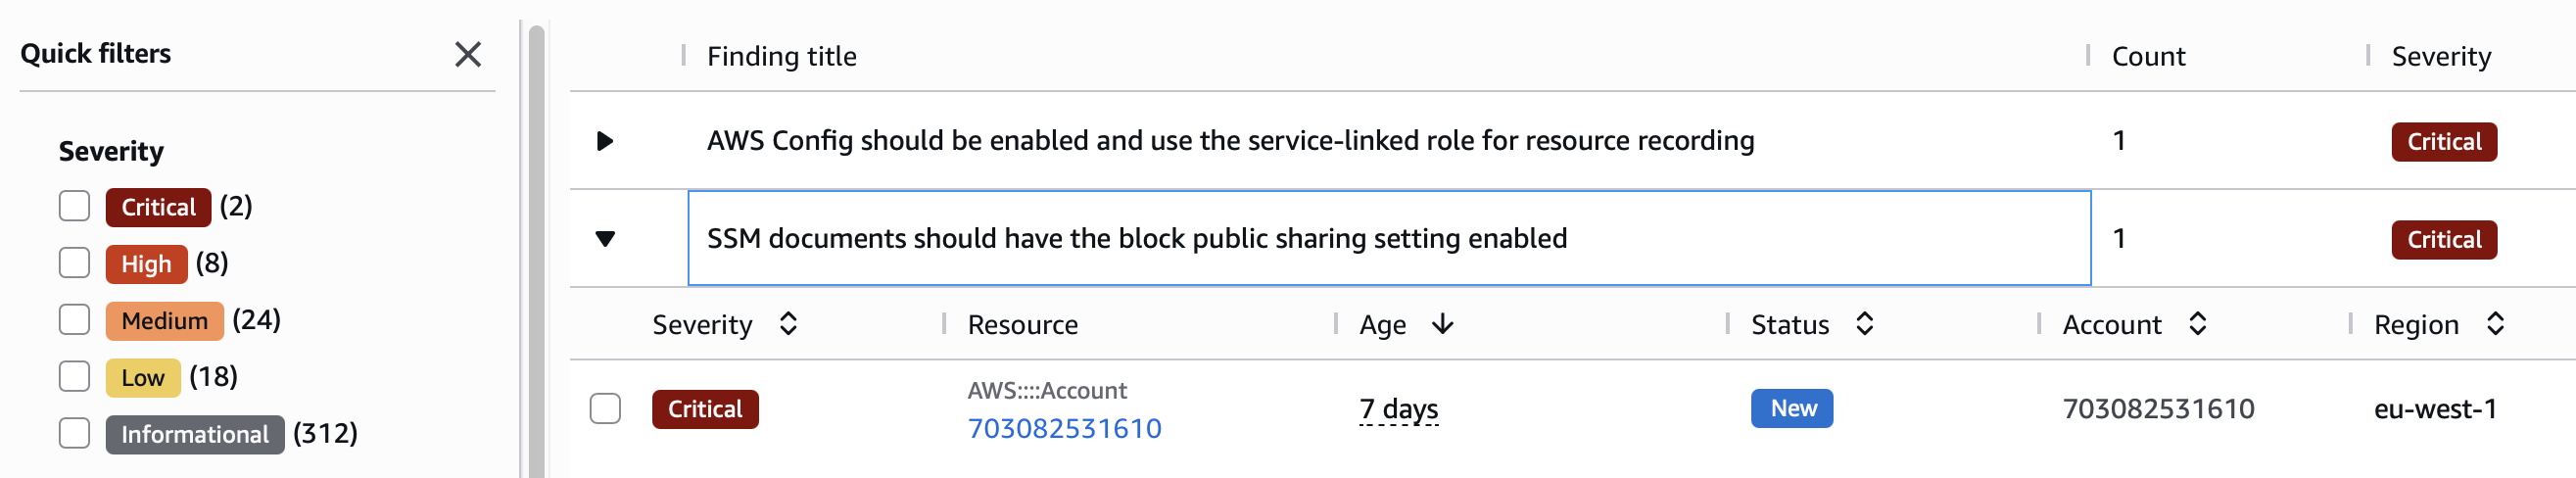
SSM documents should have the block public sharing setting enabled
Control: SSM.7
Description: This control checks whether the block public sharing setting is enabled for AWS Systems Manager documents. The control fails if the block public sharing setting is disabled for Systems Manager documents.
The block public sharing setting for AWS Systems Manager (SSM) documents is an account-level setting. Enabling this setting can prevent unwanted access to your SSM documents. If you enable this setting, your change doesn't affect any SSM documents that you're currently sharing with the public. Unless your use case requires you to share SSM documents with the public, we recommend that you enable the block public sharing setting. The setting can differ for each AWS Region.
Severity: Critical
AWS Documentation: https://docs.aws.amazon.com/systems-manager/latest/userguide/documents-ssm-sharing.html#block-public-access
How to fix it
The below will fix it only in one region. if you want to fix it for all regions within your account follow this link.
AWS CLI
Step 1
Check that you have any SSM shared documents in your region
aws ssm get-service-setting --setting-id /ssm/documents/console/public-sharing-permission --region 'us-east-1'
Command output
{
    "ServiceSetting": {
        "SettingId": "/ssm/documents/console/public-sharing-permission",
        "SettingValue": "Enable",
        "LastModifiedDate": "2021-02-03T21:05:24.747000+01:00",
        "LastModifiedUser": "System",
        "ARN": "arn:aws:ssm:us-east-1:111122223333:servicesetting/ssm/documents/console/public-sharing-permission",
        "Status": "Default"
    }
}
Step 2
Update Service setting
aws ssm update-service-setting --setting-id /ssm/documents/console/public-sharing-permission --setting-value Disable --region 'us-east-1'
No output
Step 3
Check that fixed worked
aws ssm get-service-setting --setting-id /ssm/documents/console/public-sharing-permission --region 'us-east-1'
Command output
{
    "ServiceSetting": {
        "SettingId": "/ssm/documents/console/public-sharing-permission",
        "SettingValue": "Disable",
        "LastModifiedDate": "2025-12-24T11:40:57.402000+01:00",
        "LastModifiedUser": "arn:aws:sts::111122223333:assumed-role/***********************",
        "ARN": "arn:aws:ssm:us-east-1:111122223333:servicesetting/ssm/documents/console/public-sharing-permission",
        "Status": "Customized"
    }
}
Step 4 (Optional)
Get your AWS Config evaluation rule name
aws configservice describe-config-rules --query "ConfigRules[?contains(ConfigRuleName,'ssm')].[ConfigRuleName]" --output table --region 'us-east-1'
Command output
--------------------------------------------------------------
|                     DescribeConfigRules                    |
+------------------------------------------------------------+
|  securityhub-ec2-instance-managed-by-ssm-553e7df9          |
|  securityhub-ssm-automation-block-public-sharing-60c60db5  |
|  securityhub-ssm-automation-logging-enabled-de02feb6       |
|  securityhub-ssm-document-not-public-9bb869a3              |
|  securityhub-vpc-endpoint-enabled-ssm-938782c3             |
|  securityhub-vpc-endpoint-enabled-ssm-contacts-9f45607c    |
|  securityhub-vpc-endpoint-enabled-ssm-incidents-f55289ac   |
+------------------------------------------------------------+
Re-run AWS Config evaluation rule
Re-run AWS Config control ( each config-rule-name is unique )
aws configservice start-config-rules-evaluation --config-rule-names securityhub-ssm-automation-block-public-sharing-60c60db5 --region 'us-east-1'
Check that AWS Config rule is now COMPLIANT
aws configservice describe-compliance-by-config-rule --config-rule-names securityhub-ssm-automation-block-public-sharing-60c60db5 --region 'us-east-1'
Output command
{
    "ComplianceByConfigRules": [
        {
            "ConfigRuleName": "securityhub-ssm-automation-block-public-sharing-60c60db5",
            "Compliance": {
                "ComplianceType": "COMPLIANT"
            }
        }
    ]
}
TERRAFORM
resource "aws_ssm_service_setting" "this" {
  setting_id    = "/ssm/documents/console/public-sharing-permission"
  setting_value = "Disable"
}
Best practice
Restricting access to block public sharing with IAM
You can create AWS Identity and Access Management (IAM) policies that restrict users from modifying the block public sharing setting. This prevents users from allowing unwanted access to your SSM documents.
The following is an example of an IAM policy that prevents users from updating the block public sharing setting. To use this example, you must replace the example Amazon Web Services account ID with your own account ID.
{
    "Version":"2012-10-17",
    "Statement": [
        {
            "Effect": "Deny",
            "Action": "ssm:UpdateServiceSetting",
            "Resource": "arn:aws:ssm:*:111122223333:servicesetting/ssm/documents/console/public-sharing-permission"
        }
    ]
}
Draft
aws ssm get-service-setting --setting-id /ssm/documents/allow-public-sharing --region eu-west-1
An error occurred (ServiceSettingNotFound) when calling the GetServiceSetting operation:
Security Hub treats “not set” as NON-COMPLIANT for SSM.7.
https://docs.aws.amazon.com/systems-manager/latest/userguide/documents-ssm-sharing.html#block-public-access https://support.icompaas.com/support/solutions/articles/62000223476-ensure-there-are-no-ssm-documents-set-as-public
CHECK